CVE-2026-90843
Description
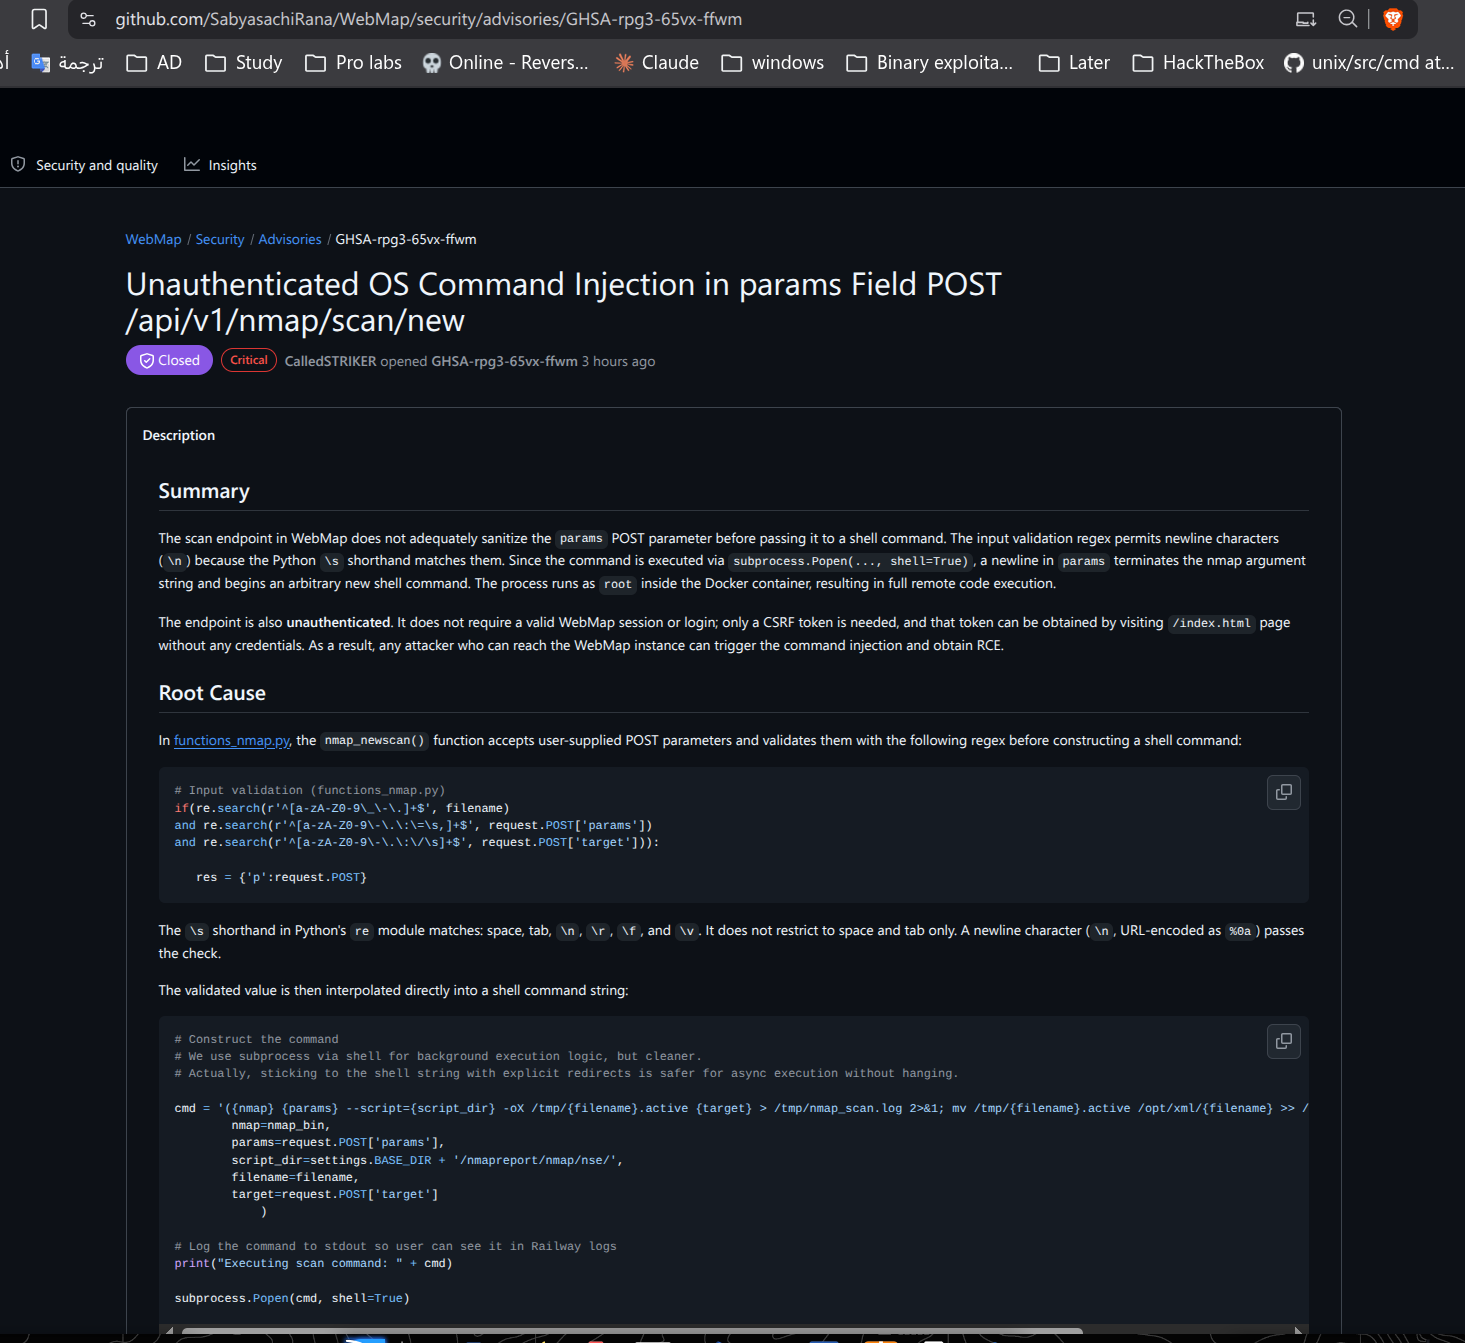
A security vulnerability has been detected in SabyasachiRana WebMap up to 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. This affects the function nmap_newscan of the file functions_nmap.py of the component New Nmap Scan Handler. Such manipulation of the argument target/params leads to os command injection. The attack may be launched remotely. The exploit has been disclosed publicly and may be used. The name of the patch is 3d52f65803a2716bff14d938352c6fef45b0cfb6. A patch should be applied to remediate this issue. This issue got fixed with a silent patch.
Severity
HIGH
CVSS v3
8.3
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:L/I:L/A:L/E:P/RL:O/RC:C · source cna
CVSS v4
6.9
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:L/VA:L/SC:L/SI:L/SA:L/E:P · source cna
Exploit chance (EPSS)
2.179%
chance of exploitation in the next 30 days
higher than 82.7% of scored CVEs · 2026-11-17
CISA KEV
Not listed
Public exploit code
Yes
Exploit references (NVD and CNA): 1
Metasploit modules: 0
Nuclei templates: 0
Weakness
- CWE-78: Improper Neutralization of Special Elements used in an OS Command
- CWE-77: Improper Neutralization of Special Elements used in a Command
CISA SSVC decision points
| Exploitation | poc |
|---|---|
| Automatable | yes |
| Technical impact | partial |
| Scored | 2026-09-16 |
Timeline
- 2026-09-15Published by the CNA00:00 UTC
- 2026-09-16CISA SSVC decision recorded1 day after publication
Affected products
Products listed as vulnerable. Upgrade to the version under "Fixed in", or a later one.
| Product | Vulnerable versions | Fixed in |
|---|---|---|
| sabyasachirana webmap |
References
- https://github.com/SabyasachiRana/WebMap/commit/3d52f65803a2716bff14d938352c6fef45b0cfb6
- https://calledstriker.gitbook.io/blog/security-research/webmap
- https://github.com/SabyasachiRana/WebMap/
- https://raw.githubusercontent.com/CalledSTRIKER/CalledSTRIKER-gitbook/refs/heads/main/security-research/2026-05-30_12-29.png
- https://vuldb.com/cve/CVE-2026-90843
- https://vuldb.com/submit/925586
- https://vuldb.com/vuln/403395
- https://vuldb.com/vuln/403395/cti
Get more CVE data from the API.
curl 'https://api.contrastcyber.com/cve_lookup/CVE-2026-90843'curl 'https://api.contrastcyber.com/cve_risk_score/CVE-2026-90843'curl 'https://api.contrastcyber.com/cve_exploit/CVE-2026-90843'curl 'https://api.contrastcyber.com/cve_products/CVE-2026-90843'
Sources
- Vulnerability data from the National Vulnerability Database (NIST) and the CVE Program. CVE records: Copyright © 1999-2026, The MITRE Corporation, used under the CVE Program Terms of Use. CVE® is a registered trademark of The MITRE Corporation.
- CWE definitions: Copyright © 2006-2026, The MITRE Corporation, used under the CWE Terms of Use. CWE is a trademark of The MITRE Corporation.
- OWASP Top 10 categories by the OWASP Foundation (CC BY 3.0).
- EPSS scores by FIRST.org EPSS, used with attribution.
- KEV catalog and SSVC decisions by CISA.
- Advisory data from the GitHub Advisory Database through OSV.dev (CC BY 4.0).
- Exploit metadata from the Exploit Database (GPL-2.0-only, metadata only).
- Nuclei template names from nuclei-templates (MIT).